Kubernetes Cluster Management: Discover Automation, Workload Scheduling, and Cluster Optimization
Kubernetes cluster management refers to the processes and technologies used to deploy, configure, monitor, secure, and maintain groups of computers that run containerized applications.
A Kubernetes cluster consists of a control plane that coordinates operations and worker nodes that execute application workloads. Containers package applications with their required dependencies, making them easier to deploy consistently across different computing environments.
As organizations adopt cloud computing, microservices, and distributed applications, managing application infrastructure becomes more complex. A single application may contain multiple services running across several machines. Kubernetes helps coordinate these workloads by automating deployment, scheduling, scaling, and recovery when certain components fail.
Cluster management includes several connected activities, such as configuring networking, allocating computing resources, managing storage, controlling access, updating software, and maintaining system availability. These activities help development and operations teams maintain reliable application environments.
A Kubernetes cluster can run in a public cloud, a private data center, an edge computing environment, or a combination of these locations. The appropriate configuration depends on application requirements, security considerations, operational expertise, and infrastructure capacity.
How a Kubernetes Cluster Works
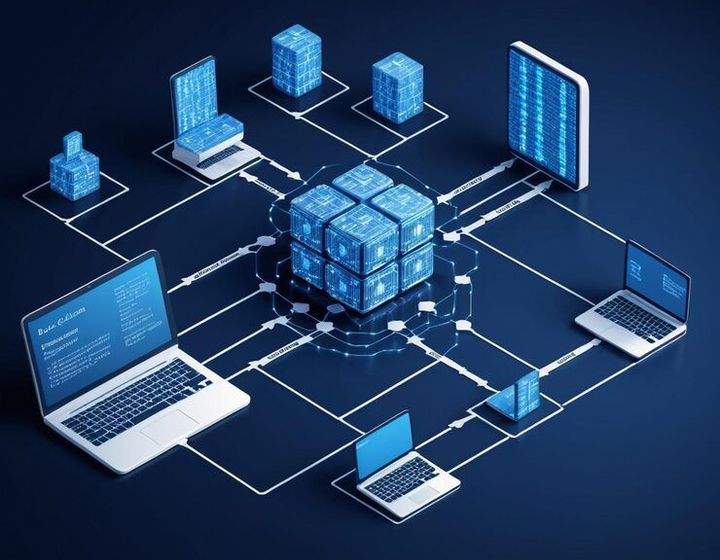
A Kubernetes cluster contains two main groups of components.
Control plane: Coordinates the cluster, maintains its desired state, and manages decisions about workloads.
Worker nodes: Run application containers through a container runtime and the Kubernetes node components.
The control plane typically includes the API server, scheduler, controller manager, and etcd database. The API server provides the main interface for cluster operations, while the scheduler selects suitable nodes for workloads. Controllers continually compare the actual cluster state with the desired configuration. Etcd stores important cluster state information.
Worker nodes run application workloads through Pods, the smallest deployable units in Kubernetes. Each Pod can contain one or more closely related containers.
For example, if a deployment specifies three application replicas, Kubernetes attempts to maintain three running instances. If a Pod fails, the relevant controllers can create a replacement, provided the cluster has sufficient resources and the application configuration permits recovery.
Why Kubernetes Cluster Management Matters
Modern applications must often remain available while handling changing workloads, software updates, and unexpected infrastructure failures. Kubernetes cluster management provides a structured way to handle these demands and helps organizations maintain consistent application environments.
Operational Reliability and Scalability
Kubernetes supports application availability by monitoring workloads and attempting to restore the desired state when components fail. Teams can configure replica counts, health checks, and automated scaling to respond to changing application needs.
Important benefits include:
Automated deployment: Applications can be deployed using declarative configuration files.
Workload scaling: Replica counts can increase or decrease according to defined requirements.
Resource allocation: CPU and memory requests help Kubernetes schedule workloads appropriately.
Failure recovery: Controllers can replace failed Pods when suitable resources are available.
Consistent environments: Standardized configurations help reduce differences between development, testing, and production.
These capabilities do not eliminate downtime automatically. Reliable operation also depends on application design, networking, storage, backups, monitoring, and the availability of underlying infrastructure.
Security and Infrastructure Governance
Kubernetes clusters can run applications that process customer records, financial transactions, business information, and internal systems. Poorly configured access permissions or exposed services may create security risks.
Cluster administrators should establish role-based access control (RBAC), network policies, container image verification, secret management, and regular security updates. Audit logs and centralized monitoring can help teams investigate unusual activity.
Infrastructure governance is also important in regulated industries. Healthcare organizations, financial institutions, government departments, and technology companies may need to demonstrate how sensitive data is protected and how operational incidents are handled.
Common Kubernetes Management Challenges
Challenge | Management approach |
|---|---|
Unexpected application failures | Health checks, replicas, and recovery policies |
Resource shortages | CPU and memory requests, limits, and capacity planning |
Unauthorized access | RBAC, identity controls, and least-privilege permissions |
Configuration differences | Version-controlled manifests and deployment automation |
Limited operational visibility | Metrics, centralized logs, and alerting |
Cluster upgrade risks | Compatibility checks, staged upgrades, and rollback planning |
Effective management combines automation with regular human review. Automated recovery can address common failures, but administrators still need to investigate recurring problems and verify that the overall system meets its reliability and security requirements.
Recent Updates and Kubernetes Management Trends
Kubernetes continues to evolve through regular releases, security improvements, API changes, and enhancements to workload scheduling. Administrators should monitor official release announcements rather than relying on outdated configuration examples.
Kubernetes Release Developments in 2026
As of October 9, 2026, the official Kubernetes release page lists versions 1.35, 1.36, and 1.37 among its actively maintained release branches. Version 1.37.1 and version 1.36.5 were both released on September 15, 2026.
A notable development in the 1.36 release cycle concerns Dynamic Resource Allocation (DRA). The project highlighted support for partitionable devices, allowing compatible hardware accelerators to be divided into logical units for allocation to workloads. This can be particularly relevant to GPU-intensive applications and AI infrastructure
These developments reflect several broader trends in cluster administration:
AI workload orchestration: Teams are improving the scheduling and allocation of GPUs and other specialized hardware.
GitOps and declarative operations: Infrastructure configuration is increasingly managed through version-controlled repositories and automated reconciliation.
Platform engineering: Organizations are creating standardized internal platforms to simplify how developers deploy and operate applications.
Security automation: Image scanning, policy enforcement, identity controls, and workload isolation are becoming important parts of deployment pipelines.
Observability: Teams are combining metrics, logs, traces, and alerts to understand application and infrastructure behavior.
What Administrators Should Review
When planning upgrades, administrators should examine API compatibility, deprecated features, add-on support, backup procedures, and security advisories. Kubernetes minor releases have defined support periods, so remaining on an outdated version can leave a cluster without ongoing maintenance and security fixes.
A practical upgrade process includes testing in a non-production environment, checking application compatibility, reviewing release notes, and confirming that backups and recovery procedures work as expected.
Laws and Policies Affecting Kubernetes Cluster Management
Kubernetes is an open-source technology, not a legal compliance framework. Organizations must configure and operate clusters in ways that meet the laws, regulatory requirements, and security obligations applicable to their activities and locations.
In India, several legal and cybersecurity frameworks may influence how Kubernetes environments are managed.
Digital Personal Data Protection Act and Rules
India's Digital Personal Data Protection Act, 2023, and the Digital Personal Data Protection Rules, 2025, establish a framework for processing digital personal data. The Rules were notified on November 14, 2025, with a phased implementation timeline.
For organizations operating Kubernetes clusters that handle personal data, relevant operational practices may include:
Applying access controls to applications and databases.
Protecting personal data through appropriate security safeguards.
Managing secrets and encryption configurations.
Maintaining incident response and data protection procedures.
Reviewing data retention, access, and deletion practices.
The exact obligations depend on the organization's role, the data involved, and the provisions in force at the relevant time.
Information Technology Act and CERT-In Directions
Organizations should assess whether these directions apply to their operations and establish appropriate security monitoring, incident escalation, and recordkeeping procedures.
Industry-Specific Requirements
Organizations in banking, healthcare, telecommunications, and government may also be subject to additional sector-specific requirements, contractual controls, or internal security standards.
Kubernetes administrators should coordinate with legal, compliance, and security teams to determine which obligations apply. Using Kubernetes, a cloud platform, or a security monitoring tool does not by itself guarantee regulatory compliance.
Tools and Resources for Kubernetes Cluster Management
Several established tools support different parts of cluster administration. The appropriate combination depends on the environment, operational complexity, and technical requirements.
Tool or resource | Primary purpose |
|---|---|
kubectl | Command-line management of Kubernetes resources |
Helm | Packaging and managing Kubernetes applications using charts |
Prometheus | Collecting and querying metrics for monitoring |
Grafana | Visualizing metrics and operational dashboards |
Argo CD | GitOps-based application deployment and reconciliation |
Kustomize | Customizing Kubernetes configuration manifests |
OpenTelemetry | Collecting and exporting telemetry, including traces and metrics |
Kubernetes official documentation | Reference guides, concepts, configuration, and upgrade information |
Frequently Asked Questions
What is Kubernetes cluster management?
Kubernetes cluster management is the process of deploying, configuring, monitoring, securing, scaling, and maintaining Kubernetes infrastructure. It includes managing worker nodes, workloads, networking, storage, permissions, and software updates.
How does Kubernetes cluster management differ from container management?
Container management focuses on running and maintaining containers. Kubernetes cluster management coordinates containerized workloads across multiple nodes and adds scheduling, service discovery, scaling, recovery, and centralized configuration capabilities.
Which tools are commonly used to manage Kubernetes clusters?
Common tools include kubectl for command-line operations, Helm for application packaging, Prometheus for metrics, Grafana for dashboards, and Argo CD for GitOps workflows. The choice depends on operational requirements and the existing technology environment.
How can Kubernetes cluster security be improved?
Security can be improved through least-privilege RBAC, network policies, trusted container images, secret management, regular patching, audit logging, and continuous monitoring. Administrators should also review exposed services and test recovery procedures.
How often should a Kubernetes cluster be upgraded?
There is no universal upgrade interval for every environment. Administrators should follow the official release lifecycle, monitor security advisories, and plan upgrades before the installed version reaches end of life. Testing, compatibility reviews, backups, and recovery planning should precede production upgrades.
Conclusion
Kubernetes cluster management helps organizations operate containerized applications across distributed computing environments. It combines workload scheduling, automated recovery, resource allocation, monitoring, security controls, and configuration management.
As Kubernetes evolves, administrators must keep up with supported releases, emerging infrastructure requirements, and changing security practices. Tools such as kubectl, Helm, Prometheus, Grafana, and Argo CD can support these activities when configured appropriately.
A well-managed cluster requires more than automation alone. Consistent documentation, tested upgrades, effective access controls, reliable monitoring, and compliance reviews help maintain a stable and secure application environment.